Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
An Abstract Interpretation-Based Deobfuscation Plugin for Ghidra ...
PCode2C: Steps Towards Translation Validation with Ghidra and CBMC ...
Ghidra Scripting, PCode Emulation, and Password Cracking - VoidStar ...
Ghidra — Скачать
Ghidra configuration // msm's home
Ghidra Review 2026: NSA Reverse Engineering Tool
GitHub - gmh5225/Ghidra-HighPCodeViewer: Ghidra plugin that adds a ...
Part 2: Reverse Engineering and Patching with Ghidra | Coalfire
Binary type inference in Ghidra - The Trail of Bits Blog
GHIDRA v9.0 (Software Reverse Engineering) - Disassemblers - Каталог ...
Ghidra Debugger
Ghidra decompiler creates High P-code containing scalars that do not ...
Automated Struct Identification with Ghidra | GRIMM Cyber R&D
Ghidra 10.2.3 keyboard shortcuts ‒ DefKey
disassembly - Can Ghidra show me the p-code generated for an ...
Ghidra 11.3 released: New features, performance improvements, bug fixes ...
GitHub - d-millar/ghidra_pcode_scripts: a few Ghidra scripts for ...
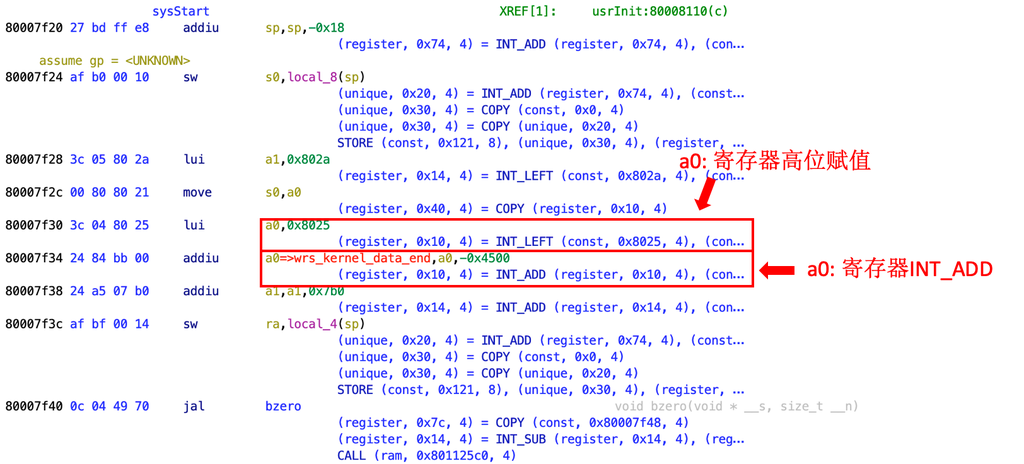
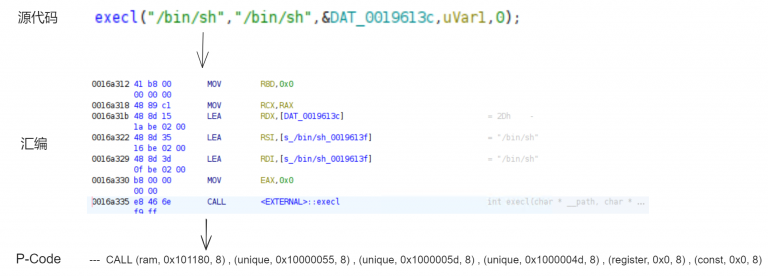
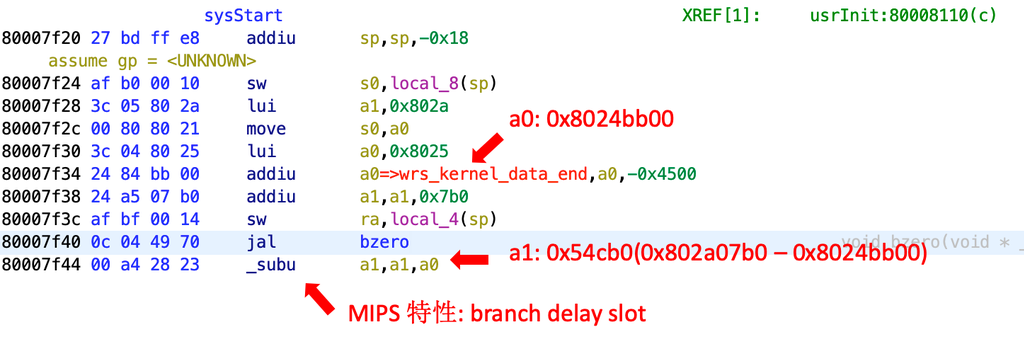
Ghidra Pcode Rewriting: 在指定位置插入或修改Pcode
(PDF) Deep Graph Neural Networks for Malware Detection Using Ghidra P-Code
How to train your Ghidra | Securelist
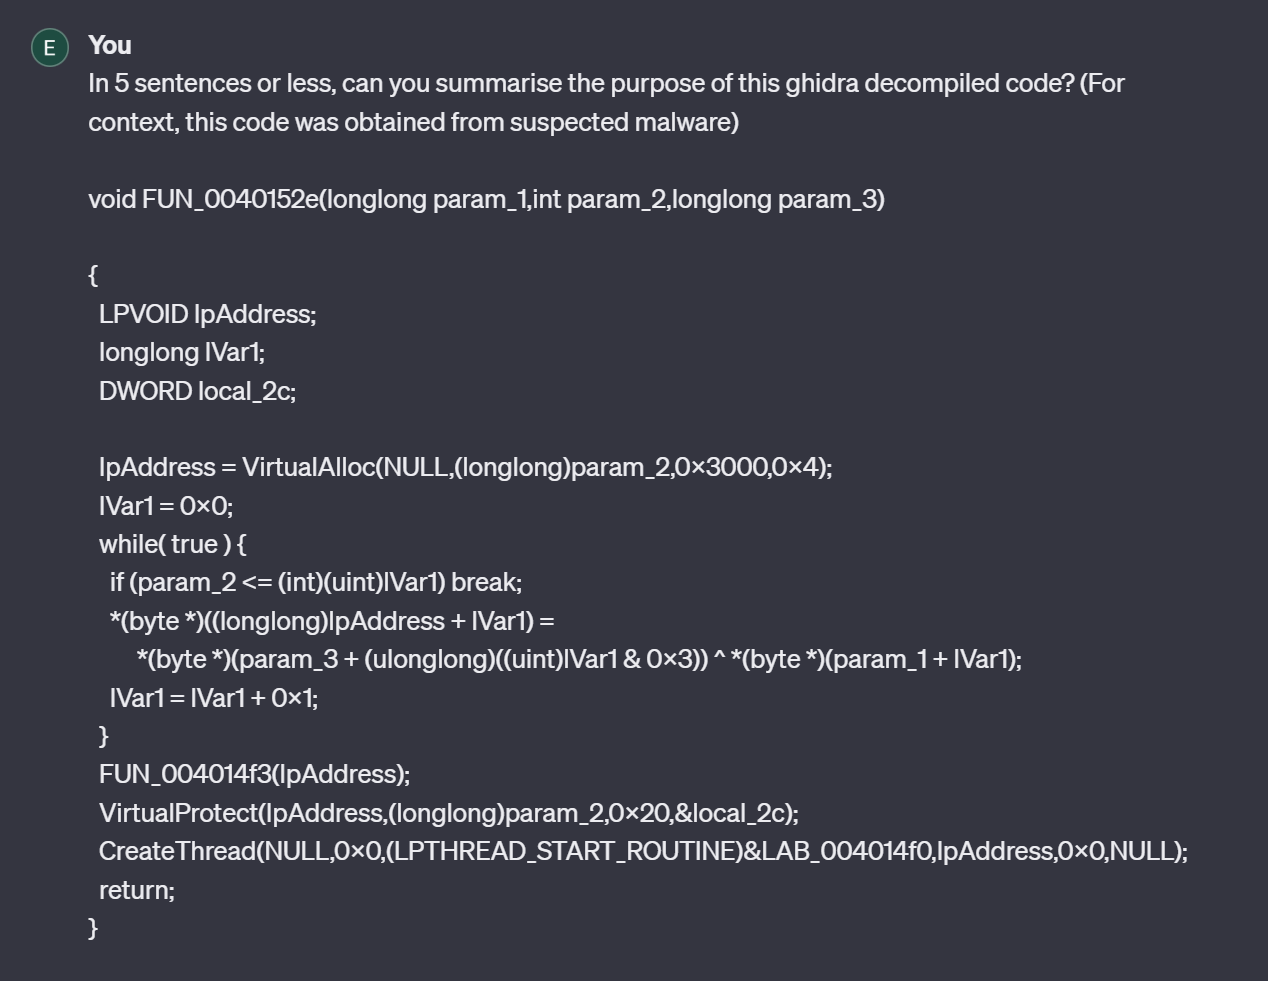
Ghidra Basics - Manual Shellcode Analysis and C2 Extraction : r/blueteamsec
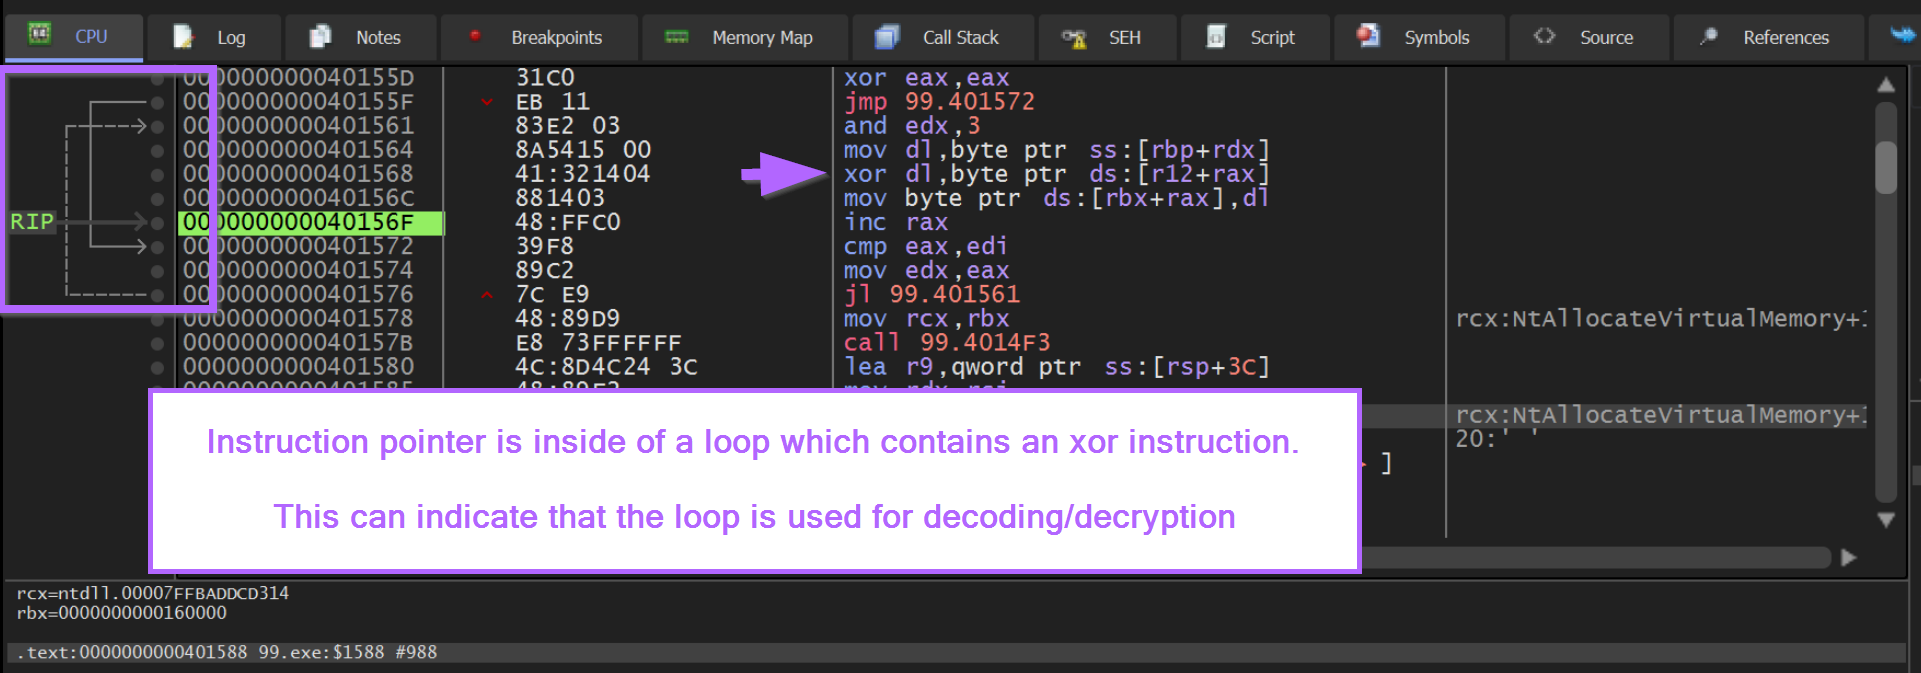
Beginner Ghidra Guide - Manual Shellcode Decryption
Ghidra
跟羽夏学 Ghidra ——数据 - 寂静的羽夏 - 博客园
GitHub - evm-sec/high-pcode: Output high level Pcode (PcodeAST) in Ghidra
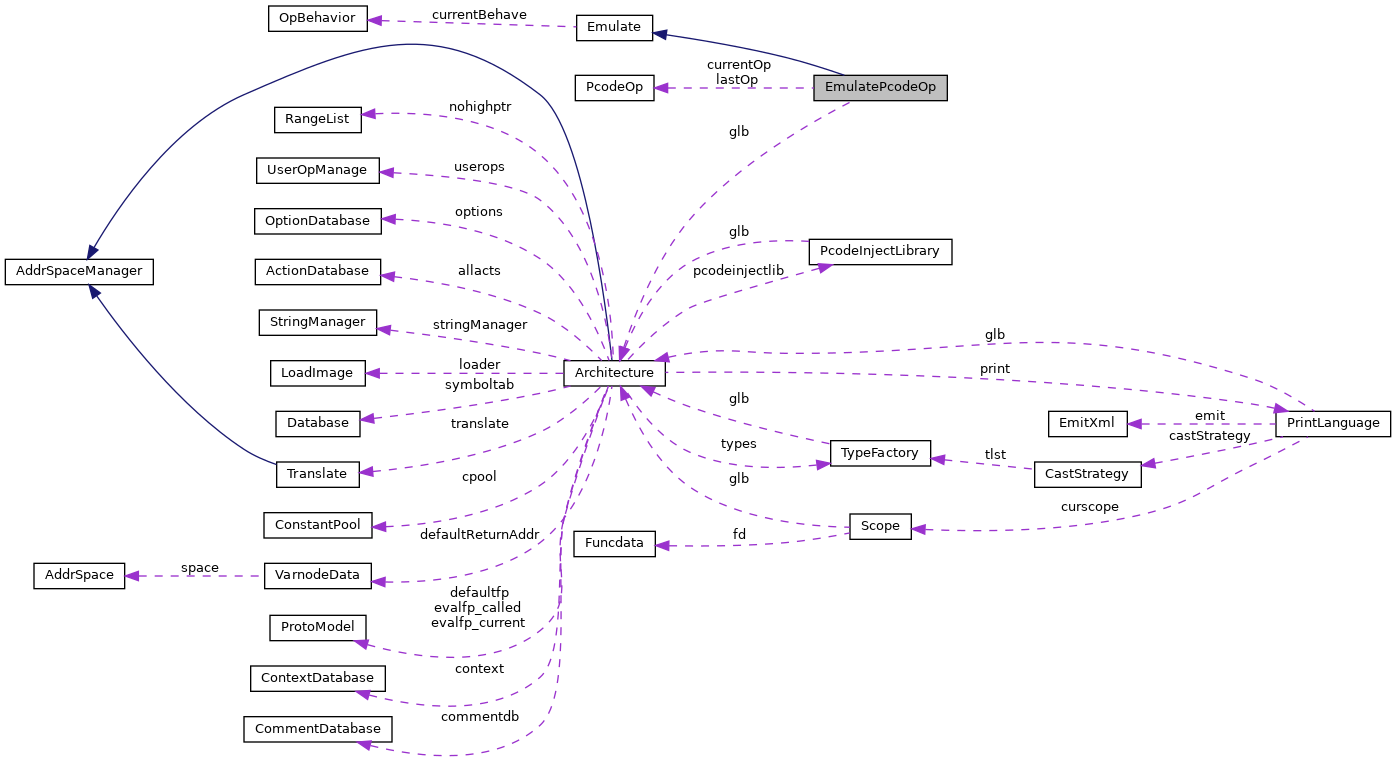
Ghidra Decompiler Analysis Engine: EmulatePcodeOp Class Reference
How to use Ghidra to Reverse Engineer Mobile Application | by K O M A L ...
Ghidra 安装与使用指南 | Blog
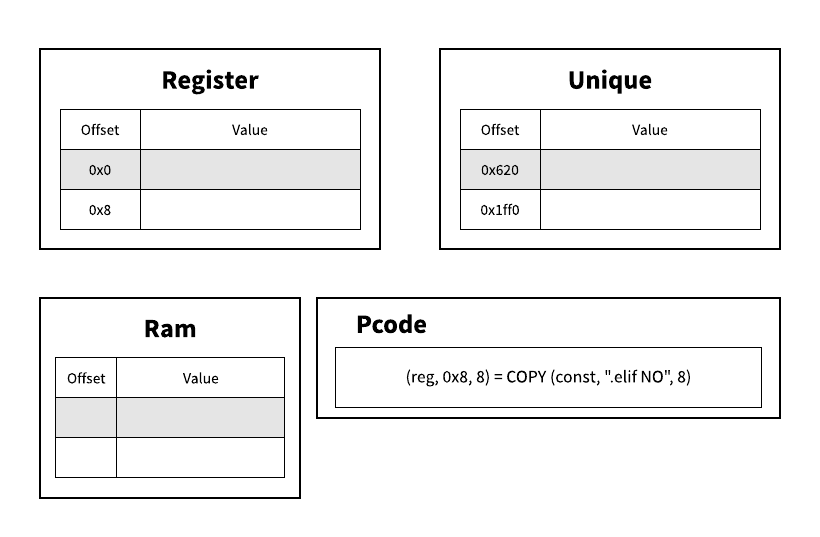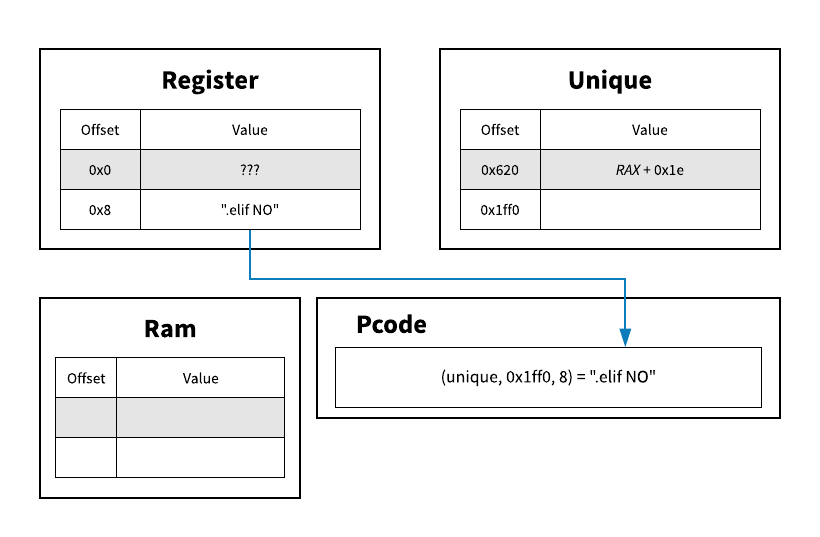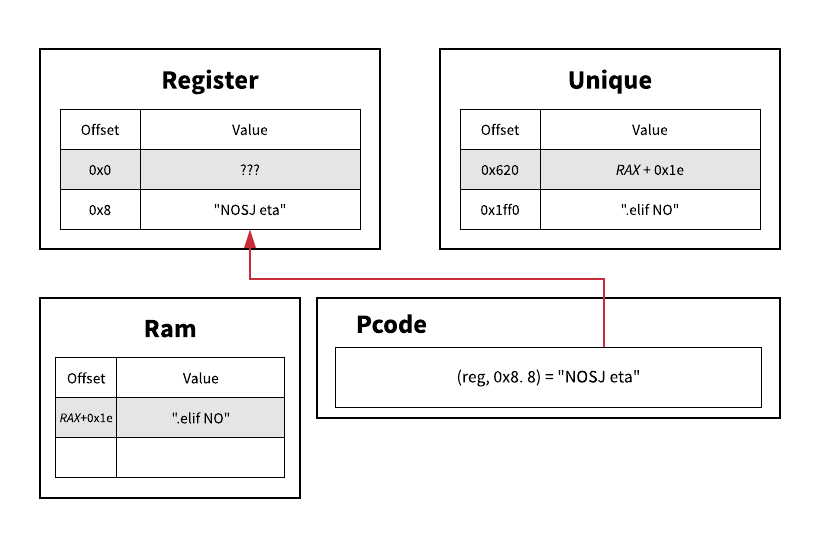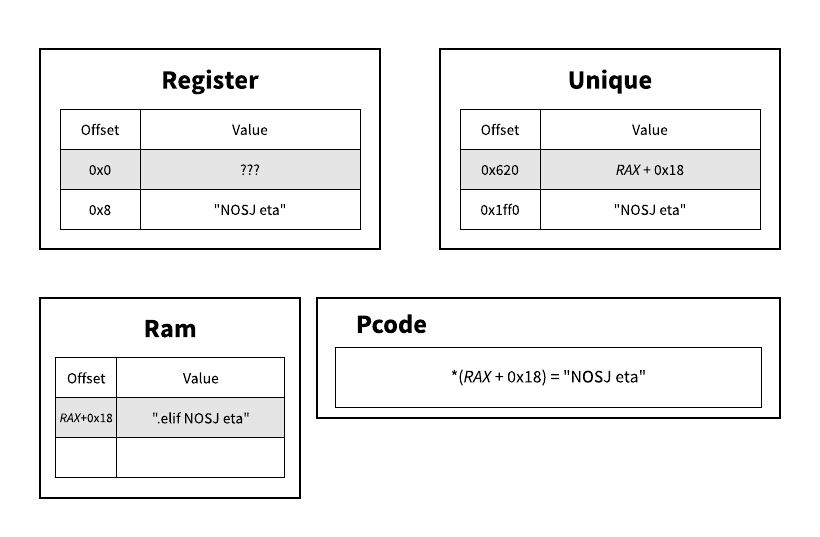
A Gentle Introduction to Static Analysis with Ghidra Pcode // v0id_deck
Guide: Ghidra Tutorial - Decompiling | HSI
Writing a Ghidra processor specification part 1 - Classic ECU
How To Use Ghidra For Malware Analysis - Establishing Context on ...
Ghidra 11.3 Released with Enhanced Features
Getting Familiar with Ghidra — Joshua McKiddy
Reverse-engineering part 6: crash course on binary patching with Ghidra ...
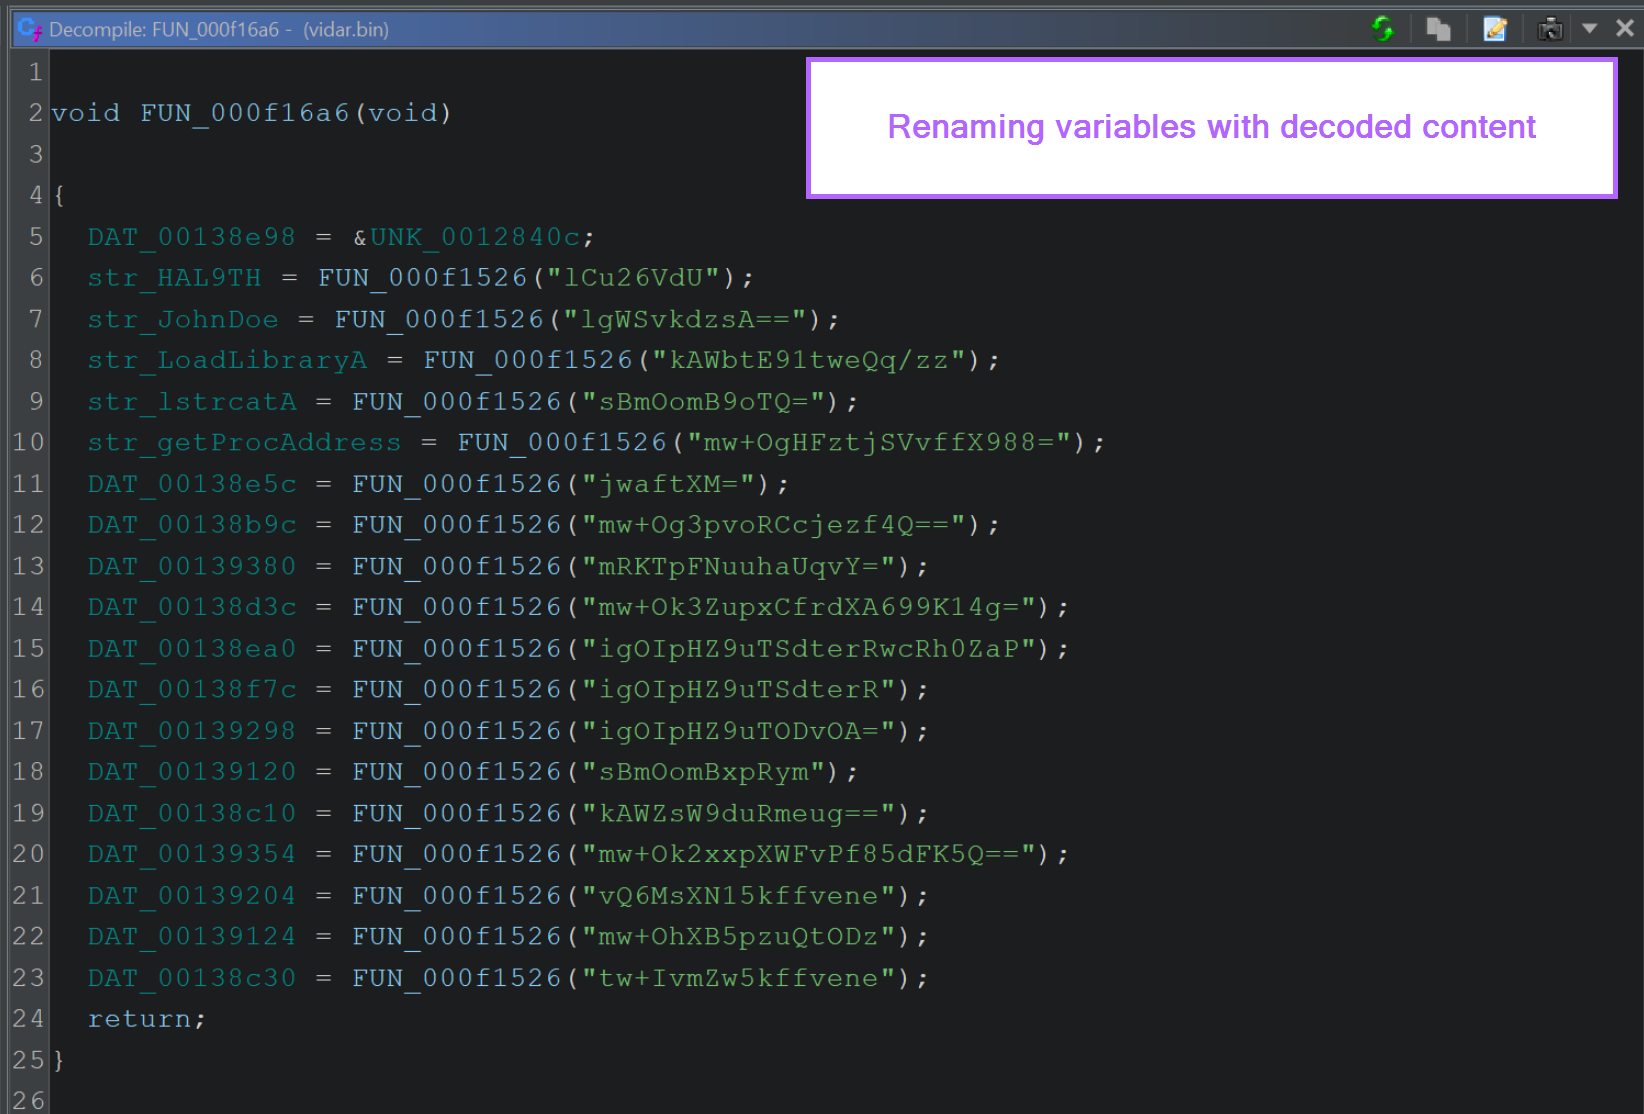
How To Use Ghidra For Malware Analysis - Identifying, Decoding and ...
Ghidra Decompiler Analysis Engine: pcodeinject.hh File Reference
Improving My Ghidra GUI + Ghidra Skills - irfan_eternal
Riding Dragons: capa Harnesses Ghidra | Google Cloud Blog
Decompiling Stack Strings in Ghidra
Ghidra | Flathub
全面详解 Ghidra - 知乎
Reverse Engineering with Ghidra
Ghidra - Download - Softpedia
GitHub - v-p-b/ghidra-vftable: Generate Ghidra class structures
Reverse Engineering macOS executables with Ghidra and Lief | DaVe's ...
Reverse Engineering a DOS Game with Ghidra and Codex | ALEX BEVILACQUA
Как приручить Ghidra | Securelist
Ian Norris - Blog - Reverse engineering with Ghidra
First Look: Ghidra 10.3 Emulator : r/ghidra
GitHub - Squirre17/ghidra-scripts: a collection of NOOB ghidra script ...
How to patch using GHIDRA - YouTube
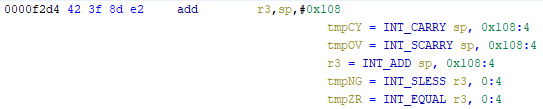
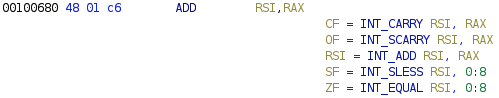
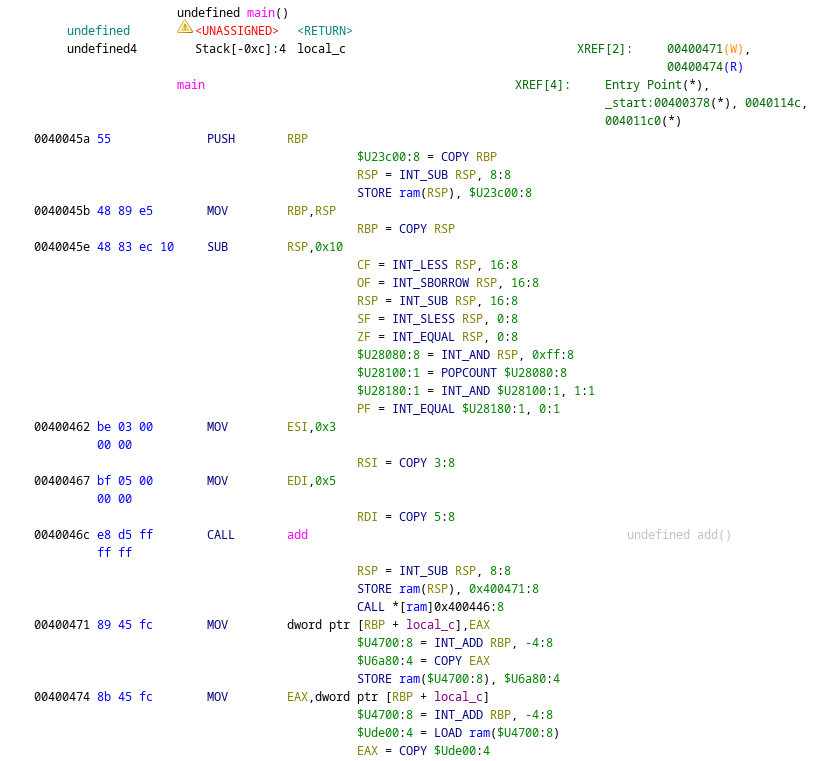
Showing the Pcode (IR instructions) between the instruction mnemonic ...
What're you telling me, Ghidra? - byte.how
Decompiler pcode manipulation over GhidraScript · Issue #1225 ...
UEFI DXE 바이너리 취약점 분석기 프로젝트_5
Ghidra: using high P-code to detect patterns in decompiler output | twevs
CS6038/CS5138 Malware Analysis, UC by ckane
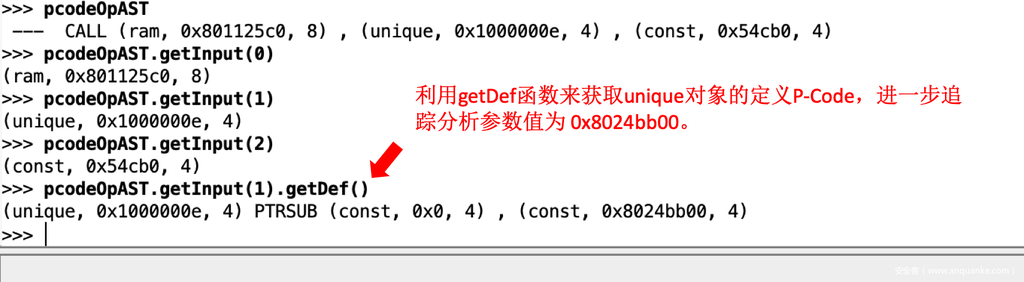
使用Ghidra P-Code进行辅助逆向分析-安全KER - 安全资讯平台
GitHub - kohnakagawa/PracticalPCode: Practical P-Code examples · GitHub
Guide to P-code Injection: Changing the intermediate representation of ...
(Raw/High) P-Code Ghidra使用的中间表示语言_ghidra pcode-CSDN博客
Figure 1 from Deep Graph Neural Networks for Malware Detection Using ...
Ghidra: ghidra::EmulatePcodeOp Class Reference
The LLRM Project - Research
Ghidra脚本编写:从IR到反编译C – 奇安信技术研究院
Working With Ghidra’s P-Code To Identify Vulnerable Function Calls
A gentle introduction to binary analysis and Ghidra's SLEIGH
Internet of Things and Data Analytics
GhidraEmu Native Pcode emulator @codeKK AndroidOpen Source Website
Medium
HWREBLOG
Nazywam (@nazywam) / Posts / X
Firmware Reversing and Analysis Tools - Thyrasec
3CX Supply Chain Compromise Leads to ICONIC Incident | Volexity
Objective-See's Blog
Lifting ISA manual reference to the processor simulator :: JNA's blog
lambdhack
Reverse Engineering
Ghidra: .../LanguageProviderPlugin/Languages.htm | Fossies
9月5日 | 英语翻译 | 《Guide to P-code Injection: Changing the intermediate ...
感謝 AI 讓我這外行人也能做簡單的逆向工程 - Huli's blog